AWS Security Specialty SCS-C03 Exam Preparation: A Practical Guide
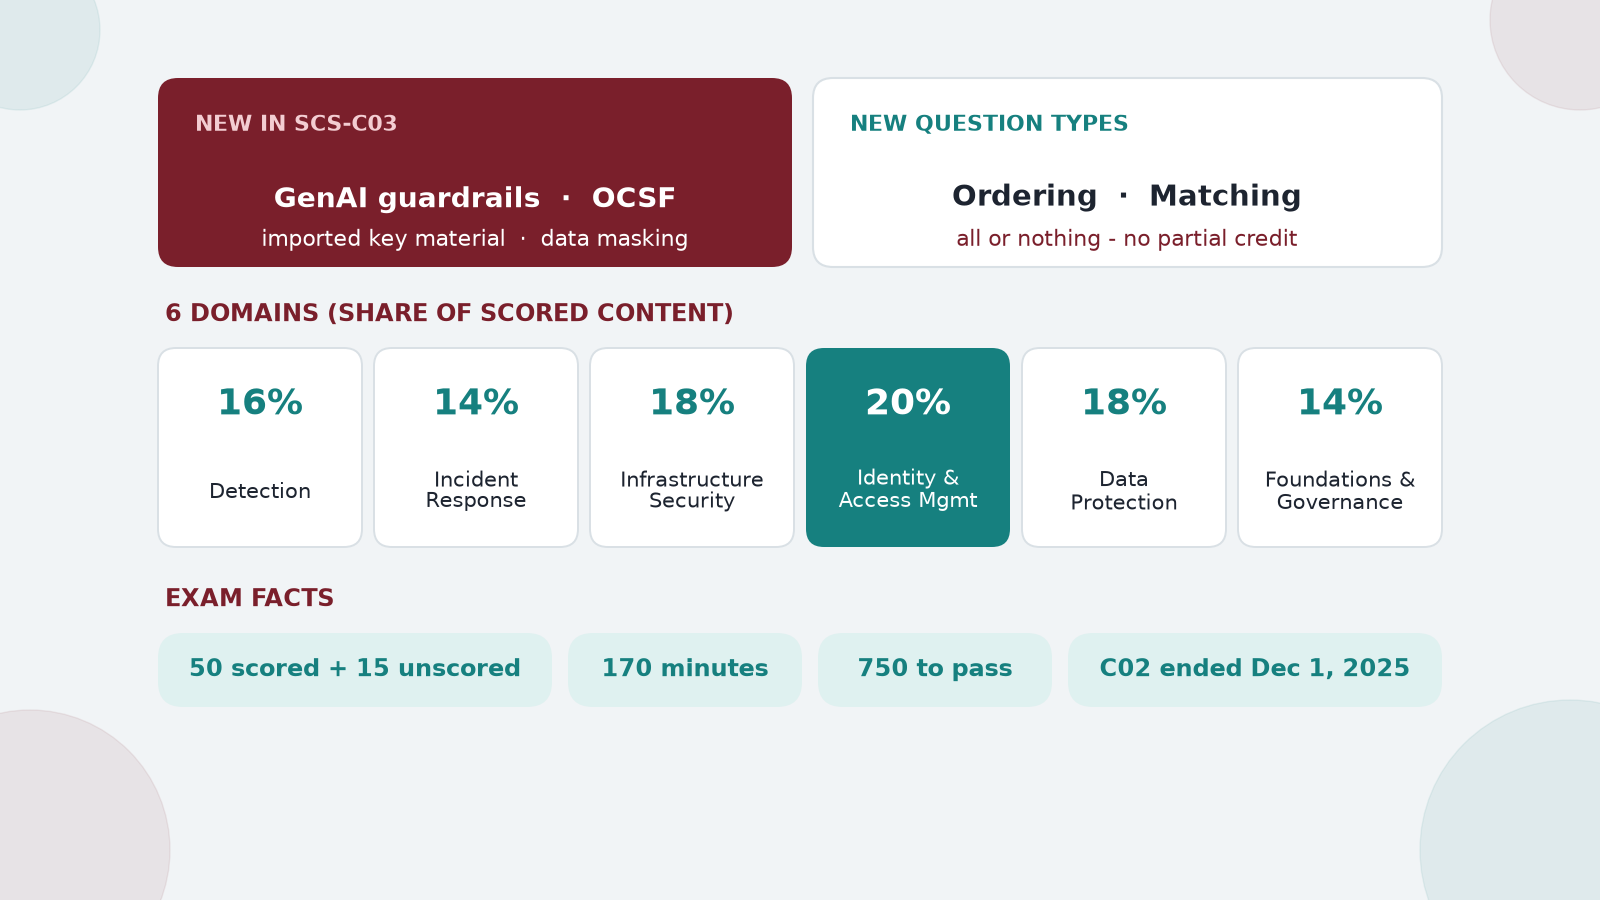
The AWS Security Specialty SCS-C03 exam replaced SCS-C02 on December 2, 2025. You get 65 questions in 170 minutes – 50 scored and 15 unscored that you can’t tell apart – and you need 750 out of 1,000. New this time: ordering and matching questions with no partial credit. I compared AWS’s C02-to-C03 appendix line by line, and what got cut matters as much as what got added.
Read more
AWS Security Specialty SCS-C03 domains and weights
| SCS-C03 domain | Weight | vs SCS-C02 |
|---|---|---|
| Detection | 16% | new split |
| Incident Response | 14% | new split |
| Infrastructure Security | 18% | was 20% |
| Identity and Access Management | 20% | was 16% |
| Data Protection | 18% | same |
| Security Foundations and Governance | 14% | renamed |
Logging moved under Detection. IAM gained the most: about 10 of the 50 scored questions, up from roughly 8.
Ordering and matching questions
Ordering asks you to pick 3-5 steps and put them in sequence. Matching pairs answers with 3-7 prompts. One wrong step or pair scores the whole question as zero. Blanks count as wrong and guessing costs nothing, so answer everything.
The AWS certification page still says “multiple choice or multiple response” only, and some prep sites copied it. The exam guide is right.
What C03 added
- GenAI app guardrails based on the OWASP Top 10 for LLM Applications
- OCSF data ingestion and third-party WAF rules
- Inter-node encryption in transit for EMR, EKS, SageMaker AI and Nitro
- Imported vs AWS-generated key material, plus data masking with CloudWatch Logs and SNS data protection policies
What got cut (most guides skip this)
ASFF, the AWS Security Incident Response Guide, CloudTrail log format, host-based firewalls and hardening, VPC Reachability Analyzer, TCP/IP and OSI basics, TLS concepts, public and private VIFs, and S3 static website hosting. Lower priority, not banned – the list isn’t exhaustive. “Components of a policy” was dropped too, but skill 4.2.3 still has you interpret IAM policies.
Odd detail: Bedrock, Q Developer, SageMaker AI, Security Lake, Verified Access and Verified Permissions sit on both the in-scope and out-of-scope lists. The task statements use several as examples, so I’d study them.
A 5-week plan
- Week 1: permission boundaries, session policies, SCPs vs RCPs, IAM Access Analyzer
- Week 2: organization CloudTrail, GuardDuty, Security Hub, Security Lake, Athena
- Week 3: isolate and snapshot an EC2 instance, Detective, WAF rate-based rules
- Week 4: KMS key policies, imported keys, multi-Region keys, Secrets Manager rotation
- Week 5: Control Tower, Config conformance packs, then timed practice
Many candidates do Solutions Architect Associate first – see our SAA-C03 guide. The cert is valid for three years. The Simplified Chinese, Latin American Spanish and Brazilian Portuguese versions retire after December 31, 2026.
Practice
Try our AWS Security Specialty practice exam. The $1 trial is deducted when you upgrade, and every plan has a 14-day money-back guarantee. Or start with the sample exam quiz.
Sources: the official SCS-C03 exam guide and its C02 comparison appendix, and the AWS certification page.